What is a multiplicative inverse?
The multiplicative inverse of a number is the value you multiply it by to get 1. For an ordinary real number a, that inverse is simply the reciprocal \(1/a\) — for example, the inverse of 4 is 0.25 because \(4 \times 0.25 = 1\). Zero has no inverse because no number times zero equals one.
$$a^{-1} = \frac{1}{\text{Number (a)}}$$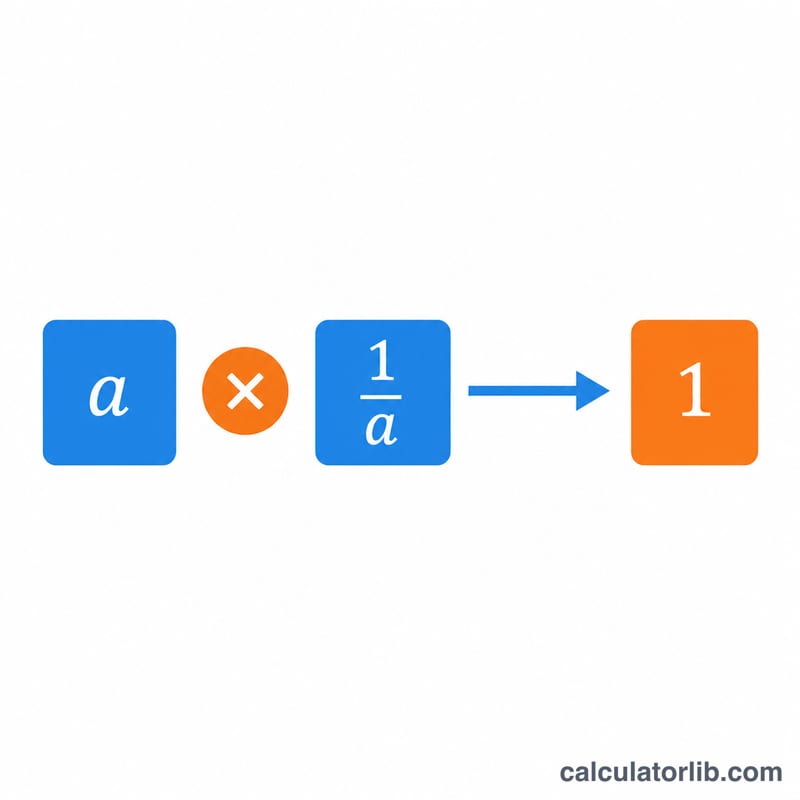
Modular inverse
In modular arithmetic, the multiplicative inverse of a (mod m) is the integer x in the range 0 to m−1 such that \(a \cdot x \equiv 1 \pmod{m}\). This appears constantly in number theory and cryptography (RSA, hashing, error-correcting codes). A modular inverse exists only when a and m are coprime — that is, \(\gcd(a, m) = 1\). This calculator finds it with the extended Euclidean algorithm.
$$\text{Number (a)} \cdot a^{-1} \equiv 1 \pmod{\text{Modulus (m)}}$$
How to use this calculator
Enter your number a. Leave the modulus at 0 (or blank) to get the plain reciprocal \(1/a\). To compute a modular inverse, enter a modulus m greater than 1; the calculator reduces a modulo m and returns the inverse, or tells you none exists if a and m share a common factor.
Worked example
Find the inverse of 3 modulo 11. We need x with \(3x \equiv 1 \pmod{11}\). Testing \(x = 4\) gives $$3 \times 4 = 12 = 11 + 1 \equiv 1 \pmod{11}.$$ So the modular inverse is 4. As a reciprocal, the inverse of 3 is \(1/3 \approx 0.333333\).
Computing a Modular Inverse by Hand with the Extended Euclidean Algorithm
The modular inverse of \(a\) modulo \(m\) is the number \(x\) with \(a \cdot x \equiv 1 \pmod{m}\). It exists only when \(\gcd(a, m) = 1\). The extended Euclidean algorithm finds it.
- Run the Euclidean algorithm on \((m, a)\). Divide repeatedly, replacing the pair \((m, a)\) with \((a, r)\), where \(r\) is the remainder, until the remainder is 0.
- Check the gcd. The last non-zero remainder is \(\gcd(a, m)\). If it is not 1, no inverse exists and you stop.
- Back-substitute through the division rows to write \(1 = a \cdot x + m \cdot y\).
- Reduce \(x\) modulo \(m\) into the range 0 to \(m-1\). Add \(m\) if \(x\) is negative.
- Verify that \(a \cdot x \bmod m = 1\).
Example: the inverse of 7 modulo 26.
| Row | Division | Quotient | Remainder |
|---|---|---|---|
| 1 | 26 = 3·7 + 5 | 3 | 5 |
| 2 | 7 = 1·5 + 2 | 1 | 2 |
| 3 | 5 = 2·2 + 1 | 2 | 1 |
| 4 | 2 = 2·1 + 0 | 2 | 0 |
The last non-zero remainder is 1, so \(\gcd(7, 26) = 1\) and the inverse exists.
Back-substitution, starting from row 3:
$$1 = 5 - 2\cdot 2$$
Substitute \(2 = 7 - 1\cdot 5\) from row 2:
$$1 = 5 - 2(7 - 5) = 3\cdot 5 - 2\cdot 7$$
Substitute \(5 = 26 - 3\cdot 7\) from row 1:
$$1 = 3(26 - 3\cdot 7) - 2\cdot 7 = 3\cdot 26 - 11\cdot 7$$
So \(x = -11\). Reducing gives \(-11 + 26 = \)15.
Verification: \(7 \cdot 15 = 105 = 4\cdot 26 + 1\), so \(105 \bmod 26 = 1\). ✓
Reciprocal vs. Modular Inverse: Example Inputs Compared
The reciprocal \(1/a\) exists for every non-zero real number. The modular inverse exists only when \(a\) and \(m\) are coprime. The two are different quantities.
| a | Modulus m | Reciprocal 1/a | Modular inverse | Note |
|---|---|---|---|---|
| 3 | 11 | 0.3333 | 4 | 3·4 = 12 ≡ 1 (mod 11) |
| 4 | 8 | 0.25 | none | gcd(4, 8) = 4, not 1 |
| 7 | 26 | 0.142857 | 15 | 7·15 = 105 ≡ 1 (mod 26) |
| −3 | 11 | −0.3333 | 7 | −3 reduces to 8 mod 11, and 8·7 = 56 ≡ 1 (mod 11) |
| 0 | any m > 1 | undefined | none | 0·x is always 0, never 1 |
The reciprocal ignores the modulus. The modular inverse is an integer in the range 0 to \(m-1\), and it exists only when \(\gcd(a, m) = 1\).
FAQ
Why does zero have no inverse? Because any number multiplied by 0 is 0, never 1.
When does a modular inverse fail to exist? When \(\gcd(a, m) \neq 1\) — for instance, 4 has no inverse mod 8 since they share the factor 4.
Can I use a negative number for modular inverse? Yes; it is first reduced into the range 0 to m−1 before inverting.